Why climate change could be catastrophic

Wrenches and sockets

The basic equation of climate change is simple enough: add greenhouse gases to the atmosphere and you warm the planet. Of course, there are endless complications in areas like changes in precipitation, sea level, etc.

There are, however, a relatively small set of reasons for which climate change could potentially enormously problematic, or even a civilizational threat. That is to say, one that has the capacity to eliminate or virtually eliminate civilizations with the major characteristics of being industrial, such as level of technological advancement and share of the population whose primary vocation is farming.

The probability of all of these is unknown, and may be very low. Still, they bear consideration when we are deciding how precautionary an approach we should take when it comes to reducing emissions. Also, more than one of these could happen simultaneously.

1) It could happen very quickly

While the normal order of business for climatic changes seems to be gradual change, there is some evidence that it is possible to cross some threshold and experience massive sudden changes. An example would be the mass melting of icecaps in Greenland and Antarctica, producing several metres of sea level rise in a matter of decades. Rapid sea level rise (albeit perhaps not to that degree) has happened before, as the result of other ‘forcings’ that affect the climate system.

More rapid change would be harder to adapt to than slower change. Rather than having to make gradual changes to how we grow food, use water, etc, we would be confronted with the immediate necessity of making big, expensive, and politically difficult changes.

2) It could take place to an extreme extent

The ultimate extreme – seeing our oceans boil away and the planet turn into a burning hell like Venus – is probably impossible. That being said, a much less dramatic change could still strain the ability of human beings to cope. There is a general consensus that warming of more than 2°C would be ‘dangerous’ and that each additional degree would heighten problems such as agricultural failure and lack of access to fresh water.

A business-as-usual course of greenhouse gas emissions that takes atmospheric concentrations to over 1000 ppm by 2100. If climate sensitivity is high (say, 8°C) then the warming that results could average 25°C above pre-industrial levels, worldwide (with more warming in high latitudes). That would surely cause massive agricultural problems and leave many areas uninhabitable. Even with sensitivity at the high end of the IPCCs probable range (4.5°C), 1000 ppm conditions could generate warming of over 15°C.

3) It could become self-sustaining

The climate system contains a number of positive feedback effects, where warming causes a change that produces more warming. Examples include sea ice melting to reveal more heat-absorbing ocean, melting permafrost releasing methane, and tropical forests drying out and burning.

If the natural world began to regularly emit more greenhouse gasses than it was removing from the atmosphere, even cutting human emissions to zero would not prevent further climate change. Our only options would be various forms of geoengineering: air capture to remove greenhouse gasses directly from the atmosphere, or techniques to alter how the planet absorbs and reflects solar radiation.

If there is a threshold beyond which runaway climate change begins, humanity might find itself trapped between facing an unknown level of warming (to stop only when the system finds a new equilibrium) or taking the desperate step of trying to actively engineer the climate.

4) It could foster conflict

Even without any of the scenarios above, it is plausible that climate change could kick off major conflicts. Bangladesh and Florida could be permanently submerged. Major river systems could see massively decreased flows. Major famines could result, etc.

If the climate changes experienced were abrupt, the danger of conflict would be further heightened, as states made desperate attempts to cope and populations relocated.

In the end, our best chance for dealing with climate change is for states to begin cooperating when they still have a good amount of time and lots of resources to direct at the issue. Also, when their will to cooperate isn’t being reduced by Hobbesian tensions. By investing reasonable amounts now in transforming our energy system and protecting carbon sinks – as well as by creating increasingly powerful incentives to reduce greenhouse gas emissions – states can not only prevent the scenarios above from occurring, they can also switch the energy basis of their society from dirty and unsustainable fossil fuels towards renewable forms of energy that can be relied upon indefinitely.

[Update: 4 February 2009] Here is a post on the danger of self-amplifying, runaway climate change: Is runaway climate change possible? Hansen’s take.
Consequences of fear and unchecked state power

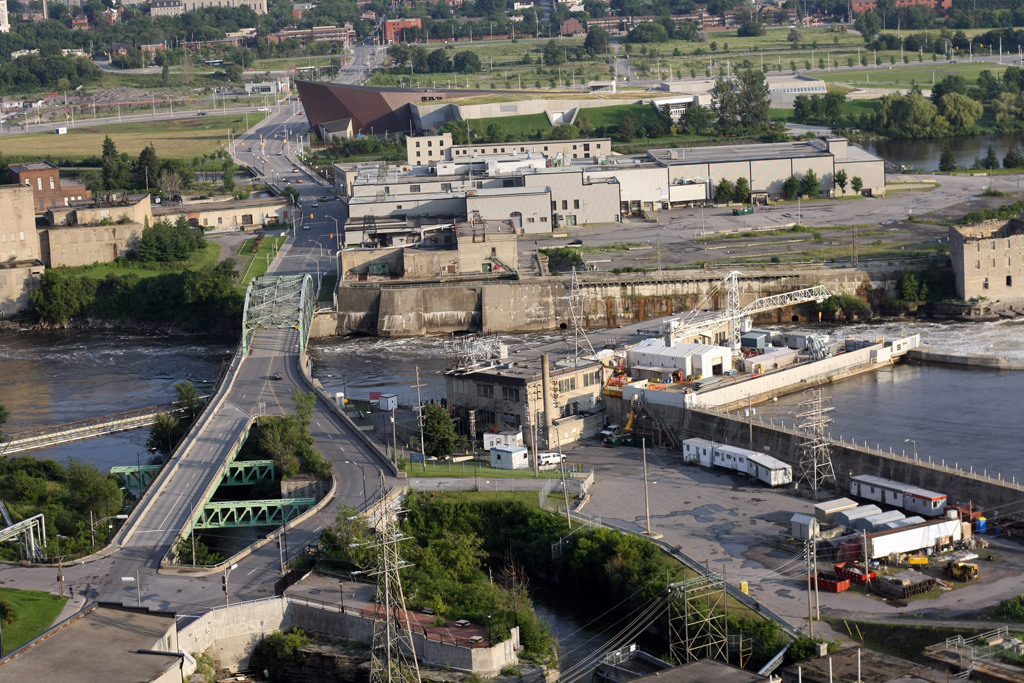
LeBreton Flats

A recent editorial on America’s sex crime laws is a nice demonstration of how the protection of the individual from the unjust application of power by the state is one of the most important kinds of human security. Pursuing criminal charges against teenagers who have sex with other teenagers – and even those who send explicit images of themselves to one another – is a lunatic way for the state to apply the law. Rather than protecting anyone, such a petty act of over-enforcement can seriously wreck the lives of those the law was intended to protect: especially when they end up on life-long public sex offender registries that do not specify what led to their initial arrest. All this becomes even more dangerous as the state gets more and more power to observe the lives of its citizens, shrinking the extent of formally private spheres (such as correspondence) where it would not previously have been watching.

It certainly bears remembering that the state is a beast that walks with a heavy, and sometimes clumsy, step. That’s something that must be borne in mind especially when the population is especially afraid of a nebulous threat, such as sex criminals or terrorists. Failing to appreciate that the application of state power can cause profound harm, as well as protection, to human security is what produces injustices like torture, Guantanamo Bay, the internment of those of Japanese descent during the Second World War, and so forth. When people are afraid, they care little about the rights of those they fear; equally damagingly, they show little appreciation for how harsh new approaches undermine the very systems they are established with the intention of protecting. Set upon the wrong course, the state is a far more dangerous entity than any terrorist organization.

Finally, there is the well-reasoned furour about the RCMP performing its own criminal investigations on officers. In any large organization, most people will act to preserve the interests of the group – even at the expense of committing injustices against outsiders. They will naturally give the benefit of the doubt to their colleagues, and they will also share loyalty with those risking their lives for the same purposes. To have any credibility, investigations into such organizations must be conducted by outsiders with independence and a strong mandate to investigate and expose wrongdoing.

Ophcrack and Windows passwords

As mentioned before, rainbow tables are a mechanism that can be used to reverse hash functions, revealing information that was intended to be hidden. For instance, they can take the hashed contents of a Windows password file and turn them into a password you can use. This limitation largely exists because Windows does not use the technique of ‘salting,’ which would make rainbow tables unmanageably large. Unix-based operating systems, like Mac OS X, have been salting passwords since the 1970s.

Ophcrack is a piece of free software that exploits precisely this vulnerability. As explained here, it comes as a bootable CD, which can be used to circumvent the password on a Windows XP, Vista, or 7 computer.

Among other things, this means that having a password-protected user account isn’t an adequate way to protect your data from anyone who can get their hands on your computer: from customs agents to burglars. If you have anything sensitive in there, it would be sensible to further protect it with some strong encryption.

In Mortal Hands

Backhoe machinery detail

Stephanie Cooke’s In Mortal Hands: A Cautionary History of the Nuclear Age is a four hundred page account of the major problems with the global nuclear industry, both civilian and military. It argues that the costs associated with both nuclear weapons and nuclear energy have been hidden by self-interested governments and organizations, and that nuclear energy should not be part of our future energy mix, despite concerns about climate change and energy security. The book’s unceasingly critical position leaves one longing for a more comprehensive account, where arguments in favour of nuclear energy would at least be more comprehensively rebutted. Nonetheless, Cooke’s book does a good job of reminding the reader of the many special dangers associated with nuclear energy, and the risks associated with re-embracing it, due to our concerns about fossil fuels.

In Mortal Hands argues convincingly that most of the costs associated with nuclear energy are hidden, and not borne by the utilities that provide it or the people that use it. These costs include wastes, contaminated sites, decommissioning of plants and related facilities, risks of accident, nuclear proliferation, providing targets to enemies and terrorists, routine radioactive emissions, the redirection of capital and expertise from potentially more positive uses, and the further entrenching of secrecy and self-serving pro-nuclear entities within government and industry. Certainly, the issue of secrecy is an important one. Along with concealing costs and subsidies, it is demonstrated that the nuclear industry has misled policy-makers and the public about the risks associated with the technologies, timelines and costs associated with the emergence of new technologies like reprocessing and ‘breeder’ reactors, and the number and severity of nuclear accidents. The industry knows that another Chernobyl or Three Mile Island could undue their anticipated ‘renaissance,’ so they are arguably less likely than ever to disclose accurate information on dangers, or on incidents which do occur. Governments that authorize, encourage, and fund new nuclear facilities will be in a similar situation, in terms of the harm awareness of risks and accidents could do to them politically.

Cooke raises a number of important points about regulation, both nationally and internationally, and the conflicts that exist between commercial pressures to get reactors sold and keep them running and concerns about safety and proliferation. None of the big nuclear states has a good record on preventing sales to states secretly working on nuclear weapons. Lack of toughness on the part of international and national regulators is a major reason why countries like Israel, South Africa, and North Korea have been able to use the cover of civilian nuclear programs to get themselves nuclear weapons. Lack of rigour is also clearly evident in nuclear programs, in terms of making sure facilities have been built and operated properly, bombs are secure, and the massive contamination is avoided.

The book is arguably weakest in its discussion of technical matters, which are not discussed at great length or in a way that seems entirely credible and convincing. Opportunities to elaborate and justify claims made about technical matters are often missed, and the book includes at least a few claims that seem likely to be erroneous. For instance, Cooke misrepresents where most of the energy in a thermonuclear explosion comes from, and fails to point out that the START-II agreement never went into effect. More than a discussion about the physics and engineering of nuclear technology, this book focuses more on the regulatory, political, and economic aspects. While that might annoy those with more technical inclinations, it is probably the right approach for a volume with the ultimate intention of informing public policy choices about whether to use nuclear energy for electricity production.

Cooke’s response to the question of how the energy currently being provided by nuclear plants could be replaced is especially unsatisfying. Essentially, it is: “Wind energy is growing very quickly, and perhaps distributed microgeneration could be the solution.” Some consideration of scale, such as that provided by David MacKay, is essential here. Small wind turbines on the roofs of houses as not a viable alternative to gigawatts worth of reactors. At the very least, those who advocate using renewables in place of nuclear need to recognize the enormous scale of deployment that would require, and the various associated costs. While Cooke’s book does not provide a sufficiently broad-minded basis for reaching a final judgment on nuclear energy, it is a convenient antidote to some of the current industry messaging that new plants will be safe and cheap, proliferation isn’t much of a concern, and even Chernobyl wasn’t so bad.

Weak-willed non-proliferation

Raw Sugar Cafe, Ottawa

Stephanie Cooke’s book In Mortal Hands: A Cautionary History of the Nuclear Age make some interesting points about the proliferation of nuclear weapons. Among them, that short-term political and commercial calculations have often overridden concerns about providing dangerous technologies to states that might aspire to developing weapons. In many cases, the examples are not hypothetical; for instance, there was Canadian and American assistance in building the CIRUS reactor that fueled India’s first atomic bombs, and America apparently played an important role in encouraging uranium mining in North Korea.

Lest people think that such shenanigans are a matter for history only, Cooke suggests that up until very recently, India faced a squeeze between being able to use uranium for plutonium production and bomb manufacture, and decided to put bombs above energy needs. The recent American decision to provide fuel to India, despite their weapons tests and rejection of safeguards against future weapons production, seems to show that we are still living in a world where civilian nuclear energy can be effectively used as a cover to advance military programs.

[Update: 8 July 2009] One correction to the above, it was apparently the International Atomic Energy Agency (IAEA) that helped North Korea develop its uranium mining program, not the United States as I indicated above. Cooke’s book does a good job of explaining how the dual role of the IAEA as both a promoter of nuclear technology and an enforcer of safeguards reduces how effectively it plays the latter role.

Effective attack against Total Position Progression (TPP) master keys

A lot of businesses and institutions rely upon master key systems, in which most keys can only open one lock, but one key can open all of them. The latter sort of keys are usually held by security personnel, superintendents, etc. One common approach to achieving this with pin tumbler locks is to put two cuts in each pin stack, instead of the usual one. That allows several different possible keys to align the cuts along a shear line, allowing the lock to be opened.

A paper by Matt Blaze, from AT&T Labs – Research, describes a relatively simple attack that foils such master key systems, allowing anyone with an ordinary key, some blanks, and a file to copy the master key without ever seeing it. Basically, the approach is to start with the non-master key, then test each pin for another value that still produces a working key. Working through pin-by-pin, you can identify where the second break lies for each pin. From that, you can file or cut yourself a key that will open all the locks in the system. Using a bit of basic math, this process can be optimized and the number of blanks and key modifications required reduced.

It’s a neat attack for a number of reasons. It doesn’t require any exotic equipment or exceptional technical skill. Nor does it require breaking into anywhere, or compromising or tricking anyone. What it does do is provide a skilled attacker with a cheap means to render a much more expensive security system ineffective, requiring the replacement of all the master locks to correct for the failure (and not just with new master locks of the same kind, which would be vulnerable again). It is also neat insofar as it demonstrates what is effectively a mathematical attack against a physical system.

It is quite possible that this attack could allow somebody with legitimate access to one unit in a group (an office, a self-storage locker, a university residence room, etc) to gain access to all others, in a way that would be hard to detect and expensive to counteract.

Weaknesses in Wiegand

Mica Prazak under an umbrella

In the past, I have identified some problems with biometrics as an element in security systems. On the Wired website, there is a relatively old article describing an attack against electronic physical access control systems, developed by Zac Franken. It exploits the fact that the commonly used Wiegand protocol – used for communication between readers and access control databases – does not perform proper authentication between the access token, reader, and database system. As a consequence, if it is possible to gain physical access to the communication wires, an attacker can record a valid exchange between a real token and the database, then replicate it to grant themselves access. It doesn’t matter if the token is a keycard, a key, or a retinal scan.

The hardware required apparently costs around $10. In addition to allowing an unauthorized user to gain access, the system can also lock out all legitimate users once the attacker is inside.

What this exploit really demonstrates is how successful security requires that every element of a system be robust against exploitation. You could spend thousands of dollars on the best biometric scanners available, only to be foiled by a simple workaround of this type.

Contributing to Project Honeypot

Spammers are one of the most annoying natural enemies of the blogging community. They waste the time of site administrators who must install anti-spam systems and dig through suspicious comments to pick out real ones. They waste the time of users who are forced to jump through hoops like site registration and CAPCHAs.

One way to help fight spam is to participate in Project Honeypot. If you run a website, they will give you a script to add somewhere. Then, you add links to the script that robots will follow, but not people. This allows the project to catalogue the IP addresses of robots, as well as track the general spam problem globally. People who run websites but don’t control the hosting (for instance, people with blogs on Blogger.com or WordPress.com) can add ‘QuickLinks’ which serve a similar function.

Stop Spam Harvesters, Join Project Honey Pot

People running WordPress blogs can also use the http:BL WordPress Plugin to take advantage of Project Honeypot’s data and block spammers and harvesters of email addresses.

Setting up a honeypot only takes a couple of minutes, and gives the satisfaction of knowing you are helping to make the internet a slightly more civil place. In addition to running a honeypot and using the http:BL plugin, this site has a wiki protected with Bad Behaviour, a blog protected with Akismet, and spam defences built into .htaccess.

Obama’s speech in Cairo

President Obama’s speech on the United States and the Muslim world, delivered in Cairo, is worth watching:

It covers the history of Islam, the United States, and the Muslim world. It also covers Afghanistan, Iraq, the Israeli-Palestinian conflict, Iran, nuclear proliferation, democracy, religious freedom, the rights of women, and economic development. Many translations are available. Climate change was not directly mentioned, despite its considerable importance for both Muslims and Americans.

At the very least, the speech demonstrates the change in tone between this administration and the last one. Whether it is the start of something more meaningful, time will tell. Slate has some commentary: relatively positive and more negative.

Hashing with Wolfram Alpha

Separately, I have discussed both the Wolfram Alpha computational knowledge engine and the practice of hashing information. The fact that WA allows anyone to do so easily has relevance for things like making bets online, in situations where players want to conceal their guesses until everyone else has put theirs up.

Here is an example. Say you want to place bets on who will win the next Republican presidential primary. You don’t want those who post later to have the advantage of knowing what others have already posted, so you do the following:

  1. Choose a hash algorithm (MD5 should be fine, but SHA is more secure)
  2. Have each participant put their guess into WA. Say I think it will be Sarah Palin. I would enter: “SHA “I think the primary winner will be Sarah Palin, though I fear what she will do with the country” into Wolfram Alpha, and it would spit out something like “f7ca 4adf 11c7 5b56 f355 1635 5b50 2eca 5950 5349”
  3. Note that the supplementary text, in addition to the name, is vital. Otherwise, it would be trivially easy for the other players to check the hashes for likely guesses and learn what people have chosen. Incorporating a salt into the hashing algorithm would be ideal, but WA doesn’t seem to have that capability.
  4. Have each participant post the hash of their response, saving the exact text somewhere secure to them.
  5. When the outcome is known, those who guessed correctly can confirm that fact, by providing text that hashes into their original post.

A somewhat roundabout and nerdy solution to a relatively unimportant problem, perhaps, but it illustrates some of the ways hashes can be used to prove what you said earlier, without having the content of your earlier message immediately accessible – a general ability with many applications.

One more fact about salts: they are the most straightforward way to foil attacks using rainbow tables.